- Marcus ReedOne person
- Workforce accountDaily work
- Marcus Reed (Admin)Privileged · IAM tasks
- User AdministratorBuilt-in role
- EA-01Emergency access
- EA-02Emergency access
Identity Secured. Access Governed.
Least privilege, on the record.
Privileged access · Scoped administration · Joiner, mover, leaver
Identity & Access Management
Hands-on Microsoft Entra ID: identity governance, RBAC, least privilege and joiner-mover-leaver lifecycle.
Identity.
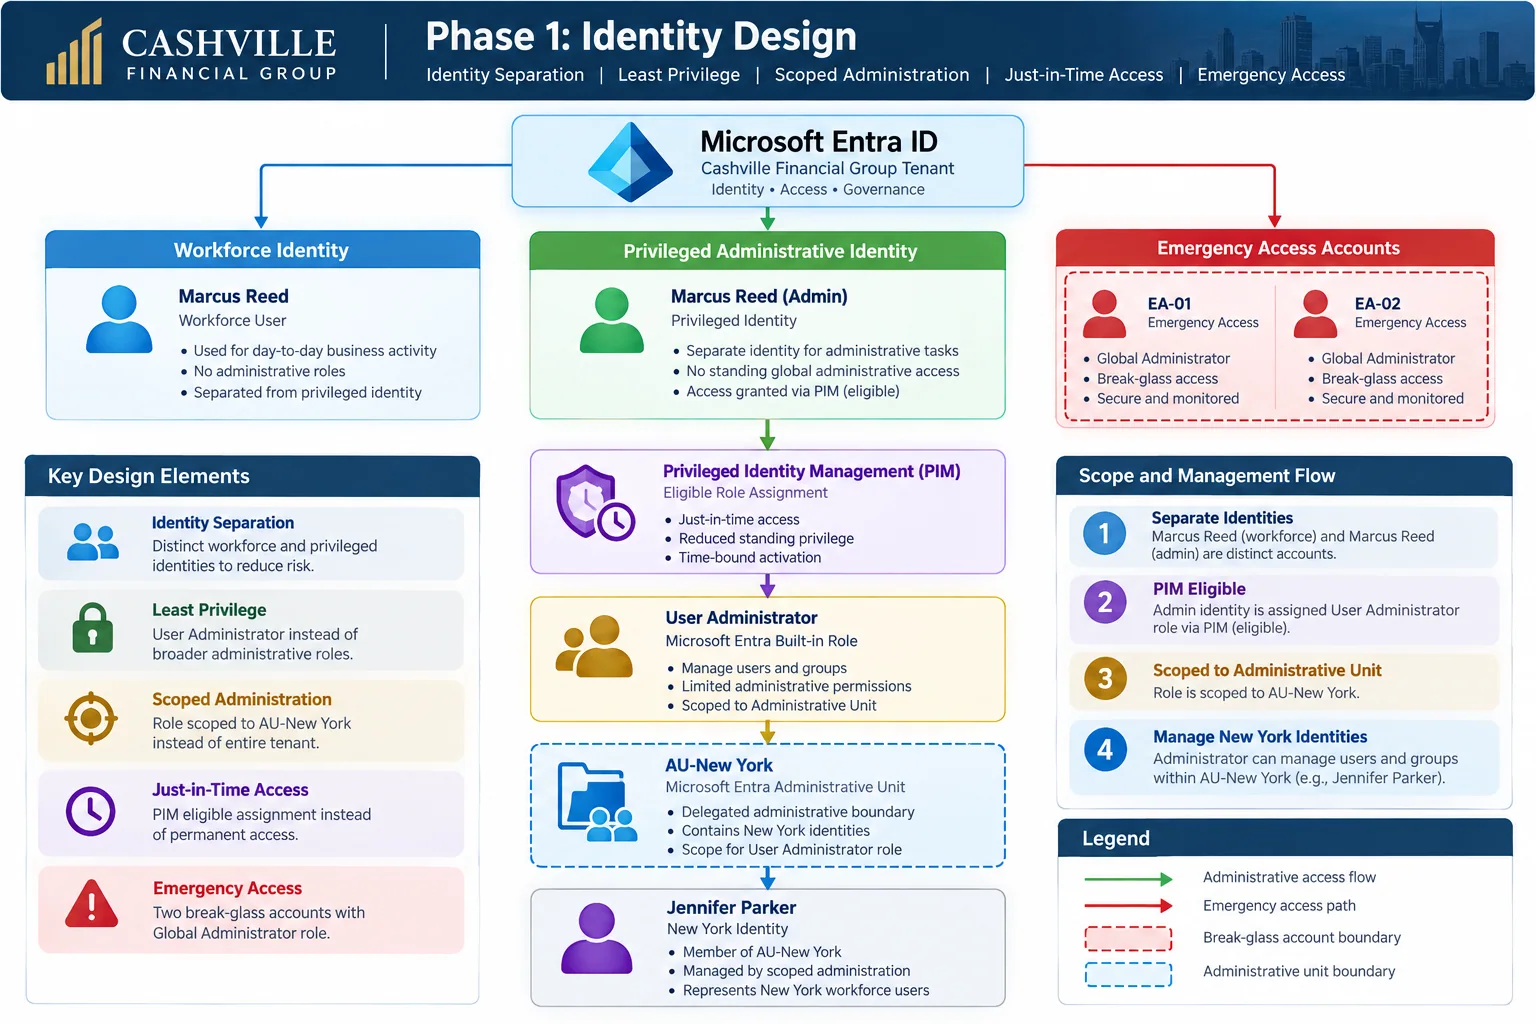
One person, two identities. Daily work never runs on privileged credentials.
Phase 1 evidence on GitHub- 01
Workforce
Marcus Reed's everyday account, used for daily work.
- 02
Privileged
A separate admin identity, Marcus Reed (Admin), used only for IAM tasks.
- 03
Emergency access
EA-01 and EA-02 hold Global Administrator for recovery only.
Privilege · CFG Phase 1
Privilege.
Control the boundary. Privileged work runs on a separate admin identity, not the everyday account.
Role is what.
User Administrator sets what Marcus Reed (Admin) can do. Unscoped, it reaches the whole tenant.
Scope is where.
AU-New York limits that role to New York identities, like Jennifer Parker.
Eligible, not standing.
The scoped role is assigned through PIM as eligible, so it is not held permanently.
Break glass, kept apart.
EA-01 and EA-02 hold Global Administrator for recovery only, outside everyday administration.
Lifecycle · CFG Phase 2
Lifecycle.
Access that follows the person. Three CFG test identities, one lifecycle.
Joiner: access granted.
Jonathan Jones joins Finance. His attributes qualify him for CFG Finance Employees, and the CFG Finance Portal follows through the group.
Created by an admin · membership evaluated by Entra ID
Mover: access adjusted.
Sarah Mitchell moves from Finance to Marketing. The rule re-evaluates, her group changes, and the inherited Finance Portal assignment disappears.
Group-derived assignment removed · no downstream deprovisioning claimed
Leaver: access revoked.
David Coleman, a contractor, never qualified for the employee-only group. His account is disabled and his Entra sessions revoked, both confirmed in the audit log.
AccountEnabled true → false · StsRefreshTokensValidFrom updated
- In studyConditional Access policy design
- In studyAuthentication methods and MFA
- In studyWorkload identities and app registrations
- In studyAccess reviews and certification
- PlannedEntitlement management and access packages
- PlannedLifecycle workflows
- PlannedHR-driven provisioning and SCIM
Validation · CFG evidence
Validation.
The evidence vault. Only completed CFG lab work is stored here.
11 capabilities. Each one on file.
Grouped by what they prove, from CFG Phase 1 and Phase 2.
Verify the work.
Select a lit panel for the redacted screenshot, the case study and the GitHub source.
- Demonstrated11Completed CFG lab evidence
- Learning4SC-300 study, not yet builtConditional Access policy design · Authentication methods and MFA · Workload identities and app registrations · Access reviews and certification
- Next3Planned hands-on labsEntitlement management and access packages · Lifecycle workflows · HR-driven provisioning and SCIM
Nothing moves up a tier without evidence.
About · The person behind the access
A.R.I.A. Out of the vault. Let me introduce the person behind the access.
01 · Foundation
Built on experience.
Three-plus years at Nissan North America supporting business-critical applications: incident investigation, root-cause analysis, and the requirements work between application owners and technical teams.
02 · Transition
Driven by identity.
My experience solving business and technology problems sparked a deeper interest in cybersecurity. Identity and access management is where I'm building my next chapter.
03 · Practice
Proven through practice.
Two CFG phases built and evidenced in Microsoft Entra ID: privileged access, then joiner-mover-leaver. Now preparing for SC-300.
I document every control like an auditor will read it.
Nissan North America
3+years supporting business-critical applications
- Systems Analyst II2022–2025
- Sr. Planner, NCAR/ICAR-X Service2025–present
Next chapter · Identity & access
- Access governance
- Least privilege
- Identity lifecycle
- Security engineering
Practiced in CFG · simulated organization
Certifications and learning
No certification is shown here as earned until it is. SC-300 is the current focus, and the case files above are where I practice its domains.
Microsoft SC-300: Identity and Access Administrator
Microsoft certification exam. Study areas:
- Implement and manage user identitiesStudying
- Implement authentication and access managementStudying
- Plan and implement workload identitiesStudying
- Plan and automate identity governanceStudying
The podcast
The Access Lounge
Exploring identity. Challenging assumptions.
A planned podcast about how access really gets granted, reviewed and removed.
AI-generated hosts
- People
- Technology
- Security
- Opportunity
In production. No episodes published yet.
Planned topics · not yet recorded
- Planned · not yet recordedJoiner, mover, leaver in plain English
- Planned · not yet recordedRole versus scope
- Planned · not yet recordedBreak glass, carefully
Feed and platform links will appear here at launch.
Next · Request accessFinal chapter · Connect
Request access.
You’ve seen the controls. Now let’s build something secure.
I’m moving into Identity and Access Management, focused on IAM Analyst, IAM Engineer and identity governance roles. Whether you’re hiring, recruiting, working in IAM or have a project in mind, email is the fastest route. My resumé has the full history.